What if the security tool you’re considering doesn’t address the risk most likely to interrupt your business? For companies weighing cybersecurity consulting Mississauga providers, the challenge isn’t finding more technology. It’s deciding which risks to tackle first and whether an adviser is building a practical plan or simply recommending another product.
That uncertainty is understandable. Security decisions affect sensitive information, client trust and day-to-day work. A useful approach should reduce exposure without adding needless complexity or disruption. Consulting should start with your business priorities, then connect recommendations to the systems and processes your team actually uses.
This guide explains what cybersecurity consulting should include and how to compare providers using clear, business-focused criteria. You’ll learn what to ask about risk assessments, recommendations and implementation, and how to identify realistic next steps. The goal is a prioritized security plan that fits your needs, not a one-size-fits-all stack of tools.
Key Takeaways
- Use a risk-first approach to focus on the systems, information and business activities that matter most.
- With cybersecurity consulting Mississauga providers, look for a clear process that connects business priorities to practical recommendations.
- Compare consultants by how they explain scope, prioritize actions and plan follow-up, not just by the tools they discuss.
- Prepare for an initial conversation by outlining your key systems, concerns and operational constraints. You don’t need a completed technical audit to get started.
Why Mississauga businesses need a risk-first cybersecurity consulting plan
Mississauga businesses don’t all have the same security priorities. A company’s size, systems, information and daily operations shape which risks could have the greatest impact. Cybersecurity consulting is expert guidance that helps a business understand its security risks, decide which ones matter most and plan practical steps to address them. That means starting with the business, not a shopping list of tools.
Buying security products before understanding the problem can add cost and complexity without addressing the most important gaps. A consultant can connect decisions to information security principles, such as protecting information from unauthorized access or loss. With cybersecurity consulting, Mississauga businesses can seek advice based on their actual systems and needs, rather than assuming one security setup suits every organization.
Which business risks should a Mississauga consultant help identify?
Start by considering how people access business systems, where sensitive data is stored, how cloud services are used and which activities would be difficult to continue if systems were disrupted. A business handling confidential client records may have different priorities from one that relies on cloud tools to deliver daily services. Ask the consultant to connect each identified risk to a business impact, such as interrupted work, exposed information or difficulty accessing an essential system. The aim is to identify meaningful exposure, not to treat every possible risk as equally urgent.
Why a security incident is also an operational concern
A security gap can affect more than technology. If staff can’t access essential systems, work may slow or stop. If information is exposed, customer confidence may suffer. The impact depends on what happened and how the business operates, so there’s no single threat profile for every organization. A risk-first plan helps leaders consider both the information they need to protect and the services they need to keep running.
What cybersecurity consulting in Mississauga should actually deliver
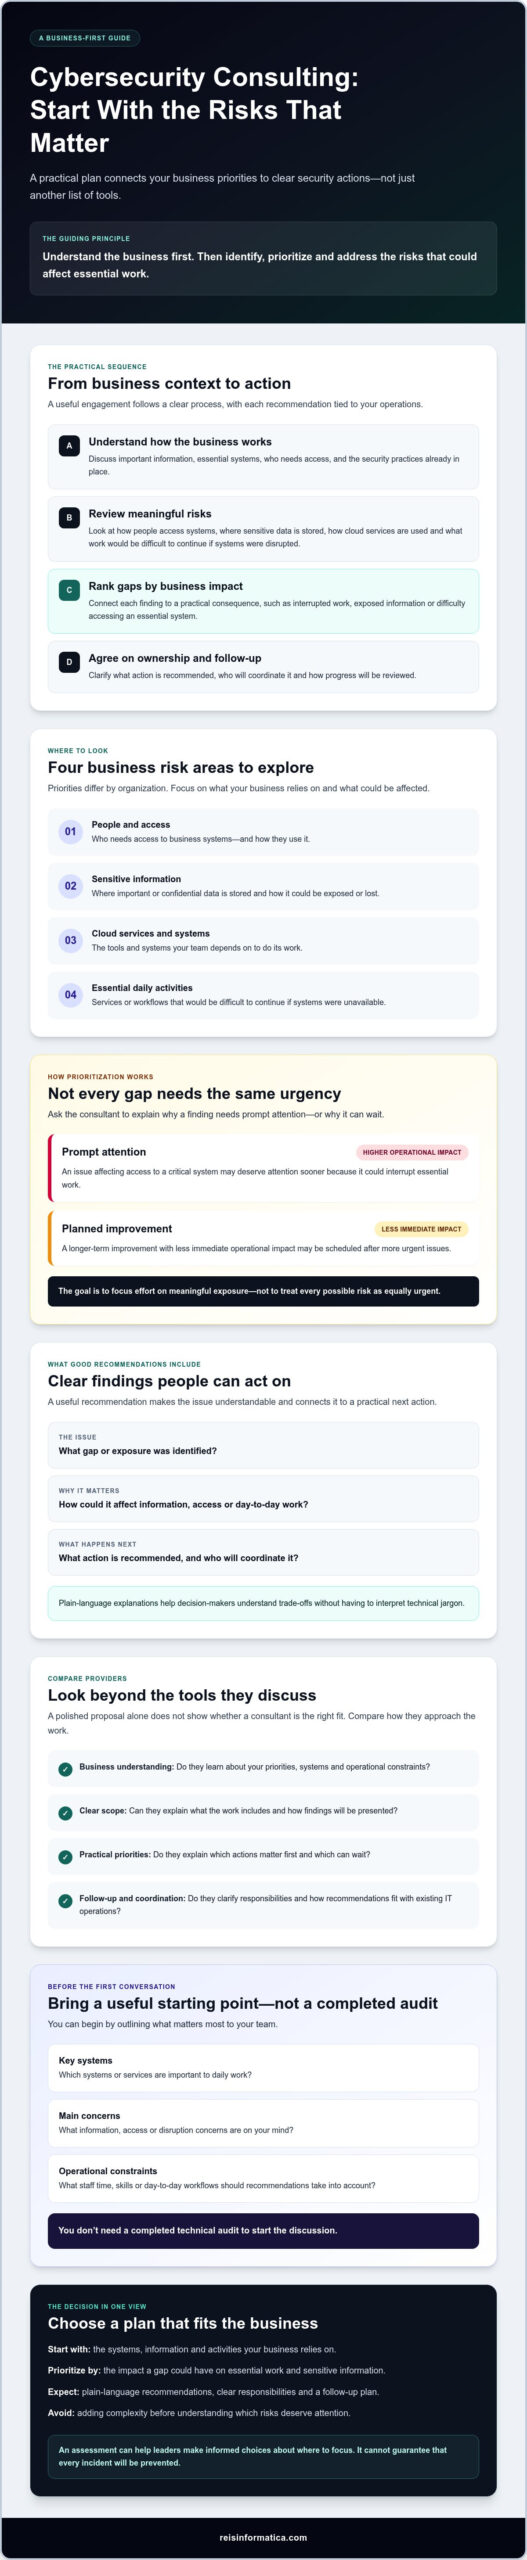
A useful engagement should follow a clear sequence: understand how the business works, review its security risks, rank the gaps, then agree on who will act and how progress will be reviewed. An assessment can highlight areas that need attention, but it can’t guarantee that every incident will be prevented. Its value is helping leaders make informed choices about where to focus.
Recommendations should fit the systems already in place, the time and skills staff can realistically contribute, and the business’s priorities. Prioritized security actions support business continuity by directing effort toward issues that could interrupt essential work. The Canadian Centre for Cyber Security also offers guidance businesses can use to inform their security planning.
From discovery to prioritized recommendations
Expect discovery questions about important information, essential systems, who needs access and the security practices already in place. A consultant should explain why a gap needs prompt attention or why it can wait. For example, an issue affecting access to a critical system may deserve attention before a longer-term improvement with less immediate operational impact.
Ask how findings will be presented, what actions are recommended and what follow-up is proposed. Useful recommendations should identify the issue, explain its relevance to your business and make the next action clear. Plain-language explanations help decision-makers understand trade-offs without having to interpret technical jargon.
How to connect security planning with daily IT operations
Security recommendations often affect the same accounts, devices, cloud services and workflows that staff rely on every day. Coordinating the plan with existing IT operations can help teams understand responsibilities and reduce avoidable disruption. If a separate provider supports your IT, clarify how security recommendations will be shared with that team and who will coordinate the work. Reis Informatica offers both cybersecurity and managed IT services. Ask how those services could fit your needs and what the proposed scope would include.
How to evaluate a cybersecurity consultant serving Mississauga
A polished proposal alone won’t tell you whether a consultant is a good fit. Compare how each provider learns about your business, explains the work, communicates findings and follows up. For cybersecurity consulting, Mississauga businesses should look for advice they can act on, not just technical terms or a list of tools.
Questions to ask before choosing a local consultant
Ask how the provider will learn about your goals, systems and operational constraints. Then clarify what you’ll receive, how recommendations will be prioritized and how progress will be reviewed. A framework such as the NIST Cybersecurity Framework can help structure a risk-based discussion, but the consultant should explain how its approach applies to your organization.
- How will you explain findings to leaders without a technical background?
- What information or time will you need from staff and existing IT partners?
- What’s included in the proposed work, and what’s excluded?
Clear answers help you understand responsibilities and avoid surprises. Confirm the scope in writing, including who owns each next step and what follow-up is part of the engagement. If a recommendation depends on another provider or on work by your own staff, ask how that dependency will be handled.
Check Canadian privacy and sector requirements carefully
Ask which privacy or sector-specific requirements may apply to your organization, the information it handles and its operations. PIPEDA may be relevant for some businesses, but it shouldn’t be treated as a blanket answer for every organization. Ask the consultant to identify questions for qualified legal or privacy advice rather than making assumptions. If staff practices are within the proposed scope, clarify whether and how they’ll be addressed.
Compare providers on fit, clear deliverables, plain-language communication and a defined review process. Reis Informatica offers cybersecurity services to businesses in Mississauga. Review Reis Informatica’s cybersecurity services as one option while assessing provider fit and scope.
Choose a Mississauga cybersecurity consulting partner and plan next steps
The right partner should fit your business, explain the scope clearly, communicate in plain language and agree on how recommendations will be reviewed. Use these criteria to compare cybersecurity consulting Mississauga providers without assuming you need every service or tool on offer.
- Business fit: Do they take time to understand your goals, systems and operational constraints?
- Transparent scope: Are the work, responsibilities and exclusions clear before you begin?
- Understandable advice: Can they explain priorities and trade-offs in terms your leadership team can act on?
- Review process: Is it clear how progress and next steps will be discussed?
Prepare for an initial cybersecurity consultation
You don’t need a completed technical audit to start a useful conversation. Bring a high-level list of important systems, business concerns and security gaps you already know about. Identify who makes decisions and who manages technology day to day. Consider what you want from the engagement, such as clear priorities, practical recommendations or a way to review progress.
Before work begins, agree on the expected scope, how updates will be shared, who will own each action and what input the consultant needs from your team or existing IT partners. This makes responsibilities clearer and helps keep the process connected to daily operations.
Connect cybersecurity planning with the right support
Reis Informatica offers cybersecurity services to businesses in Mississauga. The activities and scope for any engagement should be confirmed directly, so you can assess whether they align with your needs. If you’re comparing options in Mississauga, Kitchener, Waterloo, Cambridge, Milton, Calgary, Halifax or London, use the same questions with each provider and look for advice that’s clear, relevant and manageable for your team.
Ready to discuss your business’s cybersecurity needs? Explore Reis Informatica’s cybersecurity services and start a conversation about what your organization needs.
Take the Next Step Toward Clearer Cybersecurity Priorities
Choosing cybersecurity support doesn’t have to mean adding layers of technology or disrupting the way your team works. Start with the risks that matter to your business, then compare providers on how clearly they define the work, explain priorities and review progress. That gives you a practical basis for deciding what to address now and what can wait.
The right cybersecurity consulting Mississauga partner should connect security recommendations to your systems, staff and operational needs. Bring a short list of important systems, current concerns and questions about scope to an initial discussion. You don’t need to have every technical detail figured out before taking that step.
Reis Informatica offers cybersecurity services to businesses in Mississauga. If you’re ready to discuss your organization’s needs, talk with Reis Informatica about cybersecurity support. A clear conversation can help you identify a sensible place to begin and move forward with greater confidence.
Frequently Asked Questions
What does a cybersecurity consultant do for a small business in Mississauga?
A cybersecurity consultant helps a business understand technology-related risks, identify gaps and prioritize practical next steps. For a small business, recommendations should reflect its systems, information, staff and operational priorities, rather than assume it needs the same tools or level of support as a larger organization. Ask how the consultant works and what you’ll receive, and expect clear explanations that business leaders can understand.
How do I choose a cybersecurity consulting company in Mississauga?
Start by outlining your business priorities, important systems and current concerns, then compare how providers learn about your environment, explain findings, set priorities and follow up. Confirm the scope, responsibilities and exclusions before proceeding. For local context, Reis Informatica lists coverage in Mississauga, Kitchener, Waterloo, Cambridge, Milton, Calgary, Halifax and London. Ask any provider to explain its specific services and process in plain language.
Is cybersecurity consulting only for large companies?
No. Businesses of different sizes may benefit from outside guidance when they need help understanding security risks or deciding what to address first. The right scope depends on your operations, systems, information and existing IT resources. A useful discussion should identify what matters for your organization without assuming you need a large-company security program, a particular assessment or a standard set of tools.
What should I prepare before meeting a cybersecurity consultant?
Bring a high-level description of your business, essential systems, important information and any security concerns or recent changes. Identify who manages IT day to day and who can make decisions about recommendations. You don’t need to diagnose technical issues or complete an audit first. This background gives the consultant a starting point for useful questions and helps your leadership team assess possible next steps.
Does Canadian privacy law require my Mississauga business to hire a cybersecurity consultant?
Don’t assume that one privacy rule requires every business to hire a cybersecurity consultant. Which privacy or sector requirements may apply can depend on the organization, the information it handles and its activities. Ask a qualified legal or privacy professional to confirm what applies to your business. A consultant may discuss technical risks and safeguards, but that discussion isn’t legal advice or a guarantee of compliance.